Latest Cybersecurity News and Articles
Anthropic Expands Claude’s Enterprise Security Governance With 28 New Integrations
26 May 2026
Notable integrations include CrowdStrike, Palo Alto Networks, Microsoft, Okta, Zscaler, Netskope, Cloudflare, Fortinet, and Wiz.
The post Anthropic Expands Claude’s Enterprise Security Governance With 28 New Integrations appeared first on SecurityWeek.
Hackers Exploited KnowledgeDeliver Zero-Day for Web Shell Deployment
26 May 2026
Hardcoded machineKey values in a configuration file enabled ViewState deserialization attacks leading to remote code execution.
The post Hackers Exploited KnowledgeDeliver Zero-Day for Web Shell Deployment appeared first on SecurityWeek.
Watch on Demand: Threat Detection & Incident Response Summit – All Sessions Available
26 May 2026
Register to enjoy free access and explore the tools, strategies, and frameworks needed to build a resilient security program for a world where every minute counts.
The post Watch on Demand: Threat Detection & Incident Response Summit – All Sessions Available appeared first on SecurityWeek.
Open Source DockSec Uses AI to Cut Through Vulnerability Noise in Docker Images
26 May 2026
DockSec, an OWASP incubator project, correlates findings from multiple container security scanners and uses AI to generate plain-English remediation guidance and exact Dockerfile fixes.
The post Open Source DockSec Uses AI to Cut Through Vulnerability Noise in Docker Images appeared first on SecurityWeek.
MFA Prompt Bombing: Why Your Second Factor Isn't Saving You
26 May 2026
Multi-factor authentication (MFA) was supposed to close a critical gap in identity security. It meant that, even if an attacker possessed the account credentials, they couldn't log in without the second factor. While that logic was sound, attackers have now figured out that they don't need to steal the second factor: they just need the user to hand it over.
If your workforce authenticates with
Lithuania Suspects Foreign Involvement in Data Leak of Over 600,000 National Register Entries
26 May 2026
Lithuanian authorities are on high alert after a massive data leak involving more than 600,000 entries from national data registers.
The post Lithuania Suspects Foreign Involvement in Data Leak of Over 600,000 National Register Entries appeared first on SecurityWeek.
Admins of Bulletproof Hosting Service Used by Russian Hackers Arrested in Netherlands
26 May 2026
The two own Dutch companies that allegedly provided bulletproof hosting services to Russia-aligned threat actors.
The post Admins of Bulletproof Hosting Service Used by Russian Hackers Arrested in Netherlands appeared first on SecurityWeek.
CERT-In Mandates 12-Hour Patching for Internet-Facing Flaws Amid AI-Assisted Attacks
26 May 2026
The Indian Computer Emergency Response Team (CERT-In) has issued new guidelines requiring organizations to patch critical security vulnerabilities in internet-exposed systems within 12 hours of being flagged where "feasible" to safeguard against potential threats stemming from threat actors' abuse of artificial intelligence (AI) tools and large language models (LLMs) to automate vulnerability
Iranian Hackers Deploy MiniFast and MiniJunk V2 via Phishing and SEO Poisoning
26 May 2026
The Iranian state-sponsored threat actor known as Nimbus Manticore (aka Screening Serpens and UNC1549) has been attributed to a fresh campaign using lures impersonating organizations in the aviation and software sectors across the U.S., Europe, and the Middle East following the joint U.S.-Israeli military campaign against the country in late February 2026.
The activity, besides embracing
KnowledgeDeliver LMS Flaw Exploited to Deploy Godzilla and Cobalt Strike
26 May 2026
A now-patched high-severity security flaw affecting Digital Knowledge KnowledgeDeliver, a Learning Management System (LMS) popular in Japan, was exploited as a zero-day to deliver the Godzilla web shell and ultimately facilitate the deployment of Cobalt Strike Beacon.
The vulnerability, tracked as CVE-2026-5426 (CVSS score: 7.5), stems from the use of hard-coded ASP.NET machine keys, leading to
Nigel Farage’s Russian hack claim ‘without any merit’, former NCSC chief says
25 May 2026
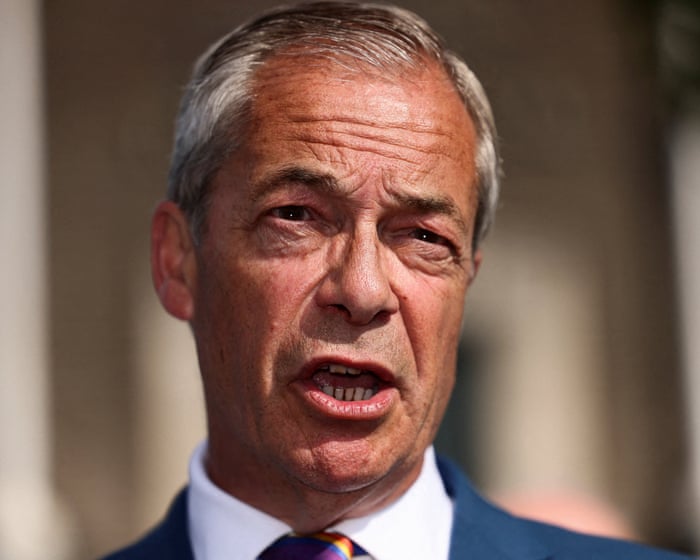 Ciaran Martin says Reform UK leader’s allegation over Guardian report on £5m gift ‘entirely unsubstantiated’Nigel Farage’s claim that a Russian hack was behind a Guardian report on the £5m gift he received from a crypto billionaire has been described as “without any merit” by a former head of the National Cyber Security Centre.Ciaran Martin, founding chief executive of the agency, which is part of GCHQ, said Farage’s allegation, if true, would have major implications for UK policy towards Russia but that the Reform UK leader had yet to provide “a shred of evidence”. Continue reading...
⚡ Weekly Recap: Linux Flaws, Defender 0-Days, Router Botnets, and Supply Chain Chaos
25 May 2026
Monday recap. Same mess, new week.
A sketchy dev tool got people pwned, old bugs came back from the dead, and security products somehow needed protecting from themselves. A bunch of companies spent the week checking old boxes and forgotten servers they should've patched years ago. Good times.
Phishing crews are getting smarter too - less obvious scam junk, more targeted stuff that actually
Ghost CMS Vulnerability Exploited to Hack Over 700 Websites
25 May 2026
Sites belonging to major universities such as Harvard and Oxford, as well as DuckDuckGo, have been compromised in the attack.
The post Ghost CMS Vulnerability Exploited to Hack Over 700 Websites appeared first on SecurityWeek.
Netherlands Seizes 800 Servers, Arrests 2 for Aiding Cyberattacks
25 May 2026
Authorities in the Netherlands have arrested the co-owners of two related Internet hosting companies for operating IT infrastructure used by Russia to carry out cyberattacks, influence operations and disinformation campaigns inside the European Union. The two men were the focus of a 2025 KrebsOnSecurity story about how their hosting companies had assumed control over the technical infrastructure of Stark Industries Solutions, an Internet service provider sanctioned last year by the EU as a frequent staging ground for cyber mischief from Russia's intelligence agencies.
Oncology Institute Discloses Data Breach
25 May 2026
The affected third-party vendor has not been named, but one possible candidate is TriZetto.
The post Oncology Institute Discloses Data Breach appeared first on SecurityWeek.
Ghost CMS CVE-2026-26980 Exploited to Hijack 700+ Sites for ClickFix Attacks
25 May 2026
Threat actors are exploiting a recently disclosed critical security flaw in Ghost CMS to inject malicious JavaScript code with an aim to fuel ClickFix attacks.
According to QiAnXin XLab, the activity involves the exploitation of CVE-2026-26980 (CVSS score: 9.4), an SQL injection vulnerability in Ghost's Content API that could allow an unauthenticated attacker to read arbitrary data from the
The Alert Firehose Finally Meets Its Match
25 May 2026
Ask a cybersecurity pro about Network Detection and Response (NDR) and you might still hear "Noisy," "Too much data." But ask the teams running NDR that includes agentic AI capabilities and you'll hear they're actually using it to catch threats earlier, triage faster, and chase fewer false positives. The old complaint lingers in part because reputations are sticky, and because NDR has evolved
266,000 Affected by Data Breach at Radiology Associates of Richmond
25 May 2026
Threat actors stole files containing names and protected health information from the healthcare organization’s systems.
The post 266,000 Affected by Data Breach at Radiology Associates of Richmond appeared first on SecurityWeek.
Anthropic: Mythos Detected 23,000 Potential Vulnerabilities Across 1,000 OSS Projects
25 May 2026
Many findings have been confirmed to be critical or high-severity vulnerabilities and the number will continue to increase.
The post Anthropic: Mythos Detected 23,000 Potential Vulnerabilities Across 1,000 OSS Projects appeared first on SecurityWeek.
Laravel-Lang Packages Poisoned for Malware Delivery
25 May 2026
Published within a 15-minute window, the malicious tags introduced backdoors to exfiltrate CI secrets.
The post Laravel-Lang Packages Poisoned for Malware Delivery appeared first on SecurityWeek.