Latest Cybersecurity News and Articles
Claude Code's “Don't Ask Again” File Exposes Passwords and Keys in 1,122 Public Copies on GitHub
07 November 2026
Passwords and API keys that developers typed into commands they approved in Claude Code are sitting in public GitHub repositories, where anyone can read them.
When a user selects "Yes, and don't ask again," Anthropic's AI coding assistant can save the command, word-for-word, including the secret, in a project settings file.
Software security company Apiiro said yesterday that 1,122 public
Activists break into building site of Microsoft datacentre in Amsterdam
06 November 2026
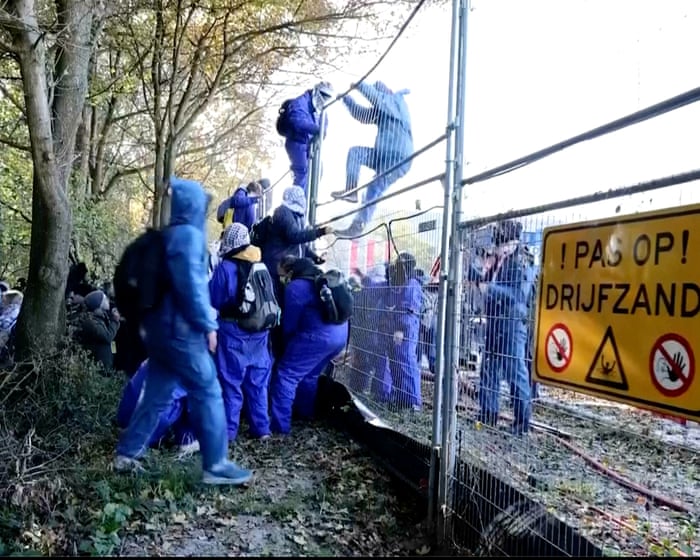 Separate actions also take place outside fence and across Europe in backlash against impact of AI boomActivists have stormed the site of a Microsoft datacentre being built in Amsterdam, as the backlash to the social and environmental harms of the AI boom spreads across Europe.Protesters from Geef Tegengas, a Dutch direct action group, clashed with police while breaking into a construction site at Westpoort, Amsterdam, where some members climbed a crane, lit flares and tied helium balloons to equipment. Continue reading...
Japan Announces Emergency Cybersecurity Package Following a Wave of Attacks
06 November 2026
The emergency package comes after dozens of companies and government agencies were hit by unauthorized access to their systems and leaks of client data, prompting uneasiness across Japan.
The post Japan Announces Emergency Cybersecurity Package Following a Wave of Attacks appeared first on SecurityWeek.
Installing the Fix for an Exploited WordPress Flaw Can Expose Some Sites One Last Time
06 November 2026
Some WordPress sites can still be attacked while they install the fix for an actively exploited flaw, according to Umut Bayram, the Picus Security researcher who found it.
The update that installs the fix still unpacks its files using the site's old, unpatched code, so an attacker who strikes at the right moment can run code on the server. The researcher advises blocking web access to the
Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot
06 November 2026
Threat actors are attempting to exploit a recently disclosed security flaw impacting OpenSSH that can enable sign-ins to accounts that have no password set, according to Previdian.
The vulnerability, tracked as CVE-2026-123158 (CVSS score: 8.1) and codenamed SSHole (or *sshole), impacts Linux systems that run OpenSSH on the musl C library with Pluggable Authentication Modules (PAM) disabled,
OpenAI Launches GPT-6 Cyber After AI Helps Find 81 Firefox Flaws, 948 Linux Exploits
06 November 2026
OpenAI on Thursday unveiled GPT‑6 Cyber, which it described as a major step forward in security research that brings together stronger cybersecurity capabilities with a step-change improvement in model alignment.
The new model is "more capable at finding and fixing vulnerabilities, and far more reliable staying within the boundaries researchers set," OpenAI said. It has classified the model as
In Other News: Trezor Implant, LLMJacking Bills Hit $1M, SAP Flaws Weaponized Within Days
06 November 2026
Noteworthy stories that might have slipped under the radar: Synology warns about NAS ransomware attacks, Flowise ‘hello’ attacks, Chainalysis breach impact expands.
The post In Other News: Trezor Implant, LLMJacking Bills Hit $1M, SAP Flaws Weaponized Within Days appeared first on SecurityWeek.
DigiCert Data Breach Impacts Business Customer Information
06 November 2026
Hackers created an account on an internal system and accessed names, email addresses, phone numbers, and business addresses.
The post DigiCert Data Breach Impacts Business Customer Information appeared first on SecurityWeek.
OpenAI Says New GPT-6 Cyber Model Hunts Flaws Without Crossing the Line
06 November 2026
Rated Critical for cybersecurity, OpenAI’s new model beats GPT-5.6 Cyber at exploitation while staying in scope more reliably.
The post OpenAI Says New GPT-6 Cyber Model Hunts Flaws Without Crossing the Line appeared first on SecurityWeek.
US Agencies Urge Organizations to Harden Refrigeration Controllers
06 November 2026
The recommendations come amid attacks targeting fridges and freezers in supermarkets and blood banks in Europe.
The post US Agencies Urge Organizations to Harden Refrigeration Controllers appeared first on SecurityWeek.
Grocery Giant Ahold Delhaize Estimates Financial Toll of October Cyberattack
06 November 2026
The October incident will cut fourth-quarter sales by up to €250 million and has led Ahold Delhaize to lower its 2026 outlook.
The post Grocery Giant Ahold Delhaize Estimates Financial Toll of October Cyberattack appeared first on SecurityWeek.
Researchers Find Residential Proxies on White House Network
06 November 2026
In a month, 28 residential proxy services used 6 addresses, mainly between 5 p.m. and midnight, Eastern Time.
The post Researchers Find Residential Proxies on White House Network appeared first on SecurityWeek.
OpenSSH Rushes Patches for ‘SSHole’ Authentication Bypass
06 November 2026
On Linux distributions using musl libc without PAM, some accounts accept any password between 257 and 1024 characters.
The post OpenSSH Rushes Patches for ‘SSHole’ Authentication Bypass appeared first on SecurityWeek.
Microsoft Paint RCE Fix Now Available, but Windows Update Won't Deliver It
06 November 2026
A fix for CVE-2026-83844, a remote code execution flaw in Windows Paint, is now in the Microsoft Store. Paint gets this fix only through a Store update, not through Windows updates.
The fixed build, 11.2609.401.0, was the newest Paint build in all ten countries The Hacker News checked today.
The flaw is an out-of-bounds read that could let an attacker run code over a network. Microsoft rates
Malicious Browser Extensions Could Use Claude Dispatch to Run Code on Users' Computers
06 November 2026
A browser extension that can run scripts on claude.ai could make Claude Desktop run code on a person's computer, researchers at Forever Security, an endpoint security company, showed in a test.
The attack needs Dispatch, a Claude feature that lets people send tasks from their phone to Claude Desktop. The flaw that makes this possible can still be exploited, the researchers said earlier this
The Flood is Coming And The Pipes Were Already Full
06 November 2026
An update on Athena, and some unsolicited predictions on what's coming next
On Saturday, Dario Amodei published We Must Pace the Frontier. I agree with him. Go read it if you haven't. I've spent the summer looking at what these models find, and the gap he describes between what they can do and what the rest of us are ready for is the one I've been staring at since May.
The hardest piece of his
OpenAI Model Wrote Its Own Network Code to Get Around Sandbox Restrictions
06 November 2026
After its sandbox proxy failed, an internal OpenAI model crafted raw packets and probed AWS services trying to reach the internet.
The post OpenAI Model Wrote Its Own Network Code to Get Around Sandbox Restrictions appeared first on SecurityWeek.
Chainalysis Breach Exposes All Users' Credentials, Forces Shutdown of Key Services
06 November 2026
Blockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cyber attack targeting its systems also exposed names, usernames, password hashes and live tokens for all users.
"While we investigated, we removed access to Reactor and Data Solutions," the company said. "At this time we continue to have no evidence that any investigations data has been accessed
Hackers Hide Linux Backdoor in Control Web Panel Server to Execute Commands Without Logs
06 November 2026
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin's XLab said this week.
The backdoored web server executes commands that attackers send via web requests, and those requests never appear in its access logs. Installing it takes root access, so the attackers must already control the server.
Experts Demonstrate Barracuda Email Security Gateway Chain Enabling Root Access Without Login
06 November 2026
Two flaws in Barracuda's Email Security Gateway, an email-filtering appliance, can be chained to run commands on it as root, its highest level of access, with no login required.
The company released patches on Monday, and the security firm watchTowr detailed the attack chain on Thursday.
One flaw, CVE-2026-116606, is an authorization bypass. An unauthenticated attacker can use it to restore a