Latest Cybersecurity News and Articles
CTEM is the New SOC: Shifting from Monitoring Alerts to Measuring Risk
13 June 2025
Introduction: Security at a Tipping Point
Security Operations Centers (SOCs) were built for a different era, one defined by perimeter-based thinking, known threats, and manageable alert volumes. But today’s threat landscape doesn’t play by those rules. The sheer volume of telemetry, overlapping tools, and automated alerts has pushed traditional SOCs to the edge. Security teams are overwhelmed,
Fog Ransomware Attack Employs Unusual Tools
13 June 2025
Multiple legitimate, unusual tools were used in a Fog ransomware attack, including one employed by Chinese hacking group APT41.
The post Fog Ransomware Attack Employs Unusual Tools appeared first on SecurityWeek.
Critical Vulnerability Exposes Many Mitel MiCollab Instances to Remote Hacking
13 June 2025
Mitel has announced patches for a MiCollab path traversal vulnerability that can be exploited remotely without authentication.
The post Critical Vulnerability Exposes Many Mitel MiCollab Instances to Remote Hacking appeared first on SecurityWeek.
Critical Vulnerabilities Patched in Trend Micro Apex Central, Endpoint Encryption
13 June 2025
Trend Micro patches critical-severity Apex Central and Endpoint Encryption PolicyServer flaws leading to remote code execution.
The post Critical Vulnerabilities Patched in Trend Micro Apex Central, Endpoint Encryption appeared first on SecurityWeek.
ZeroRISC Raises $10 Million for Open Source Silicon Security Solutions
13 June 2025
ZeroRISC has raised $10 million in seed funding for production-grade open source silicon security, built on OpenTitan designs.
The post ZeroRISC Raises $10 Million for Open Source Silicon Security Solutions appeared first on SecurityWeek.
Apple Zero-Click Flaw in Messages Exploited to Spy on Journalists Using Paragon Spyware
13 June 2025
Apple has disclosed that a now-patched security flaw present in its Messages app was actively exploited in the wild to target civil society members in sophisticated cyber attacks.
The vulnerability, tracked as CVE-2025-43200, was addressed on February 10, 2025, as part of iOS 18.3.1, iPadOS 18.3.1, iPadOS 17.7.5, macOS Sequoia 15.3.1, macOS Sonoma 14.7.4, macOS Ventura 13.7.4, watchOS 11.3.1,
Inside a Dark Adtech Empire Fed by Fake CAPTCHAs
12 June 2025
Late last year, security researchers made a startling discovery: Kremlin-backed disinformation campaigns were bypassing moderation on social media platforms by leveraging the same malicious advertising technology that powers a sprawling ecosystem of online hucksters and website hackers. A new report on the fallout from that investigation finds this dark ad tech industry is far more resilient and incestuous than previously known.
WordPress Sites Turned Weapon: How VexTrio and Affiliates Run a Global Scam Network
12 June 2025
The threat actors behind the VexTrio Viper Traffic Distribution Service (TDS) have been linked to other TDS services like Help TDS and Disposable TDS, indicating that the sophisticated cybercriminal operation is a sprawling enterprise of its own that's designed to distribute malicious content.
"VexTrio is a group of malicious adtech companies that distribute scams and harmful software via
Advanced AI Experiences “Complete Accuracy Collapse” When Given Complex Problems
12 June 2025
When given highly complex problems, AI models failed to provide correct answers.
Paragon ‘Graphite’ Spyware Linked to Zero-Click Hacks on Newest iPhones
12 June 2025
Citizen Lab publishes forensic proof that spyware maker Paragon can compromise up-to-date iPhones. Journalists in Europe among victims.
The post Paragon ‘Graphite’ Spyware Linked to Zero-Click Hacks on Newest iPhones appeared first on SecurityWeek.
The AI Arms Race: Deepfake Generation vs. Detection
12 June 2025
AI-generated voice deepfakes have crossed the uncanny valley, fueling a surge in fraud that outpaces traditional security measures. Detection technology is racing to keep up.
The post The AI Arms Race: Deepfake Generation vs. Detection appeared first on SecurityWeek.
Rinki Sethi Hired as Chief Security Officer at Upwind
12 June 2025
Rinki Sethi has been hired as Chief Security Officer at Upwind. In this role, Sethi will lead Upwind’s global information security and technology functions.
New TokenBreak Attack Bypasses AI Moderation with Single-Character Text Changes
12 June 2025
Cybersecurity researchers have discovered a novel attack technique called TokenBreak that can be used to bypass a large language model's (LLM) safety and content moderation guardrails with just a single character change.
"The TokenBreak attack targets a text classification model's tokenization strategy to induce false negatives, leaving end targets vulnerable to attacks that the implemented
AI Agents Run on Secret Accounts — Learn How to Secure Them in This Webinar
12 June 2025
AI is changing everything — from how we code, to how we sell, to how we secure. But while most conversations focus on what AI can do, this one focuses on what AI can break — if you’re not paying attention.
Behind every AI agent, chatbot, or automation script lies a growing number of non-human identities — API keys, service accounts, OAuth tokens — silently operating in the background.
And here’s
Hirundo Raises $8 Million to Eliminate AI’s Bad Behavior
12 June 2025
Hirundo tackles AI hallucinations and bias by making trained models “forget” poisoned, malicious, and confidential data.
The post Hirundo Raises $8 Million to Eliminate AI’s Bad Behavior appeared first on SecurityWeek.
Security Leaders Discuss the Whole Foods Distributor Cyberattack
12 June 2025
Security leaders discuss the Whole Foods distributor cyberattack, with insights on attacker motivations as well as risk mitigation strategies.
New ‘SmartAttack’ Steals Air-Gapped Data Using Smartwatches
12 June 2025
The new attack technique uses smartwatches to capture ultrasonic covert communication in air-gapped environments and exfiltrate data.
The post New ‘SmartAttack’ Steals Air-Gapped Data Using Smartwatches appeared first on SecurityWeek.
European journalists targeted with Paragon Solutions spyware, say researchers
12 June 2025
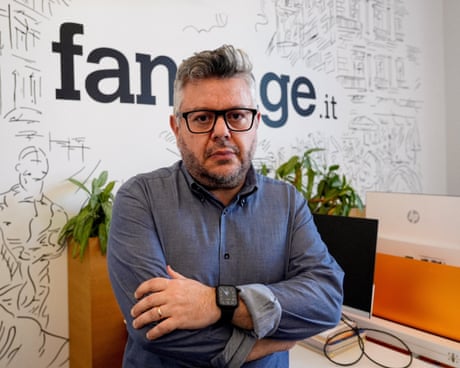 Citizen Lab says it found ‘digital fingerprints’ of military-grade spyware that Italy has admitted using against activistsThe hacking mystery roiling the Italian prime minister Giorgia Meloni’s rightwing government is deepening after researchers said they had found new evidence that two more journalists were targeted using the same military-grade spyware that Italy has admitted to using against activists.A parliamentary committee overseeing intelligence confirmed earlier this month that Italy had used mercenary spyware made by Israel-based Paragon Solutions against two Italian activists. Continue reading...
Zero-Click AI Vulnerability Exposes Microsoft 365 Copilot Data Without User Interaction
12 June 2025
A novel attack technique named EchoLeak has been characterized as a "zero-click" artificial intelligence (AI) vulnerability that allows bad actors to exfiltrate sensitive data from Microsoft 365 Copilot's context sans any user interaction.
The critical-rated vulnerability has been assigned the CVE identifier CVE-2025-32711 (CVSS score: 9.3). It requires no customer action and has been already
‘EchoLeak’ AI Attack Enabled Theft of Sensitive Data via Microsoft 365 Copilot
12 June 2025
Microsoft recently patched CVE-2025-32711, a vulnerability that could have been used for zero-click attacks to steal data from Copilot.
The post ‘EchoLeak’ AI Attack Enabled Theft of Sensitive Data via Microsoft 365 Copilot appeared first on SecurityWeek.