Latest Cybersecurity News and Articles
UK and FBI take over ransomware group’s website
20 February 2024
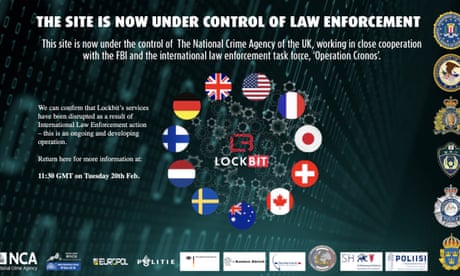 UK agency says they have ‘hacked the hackers’ and will help LockBit victims decrypt their systemsA massive law enforcement operation has seized the “command and control” infrastructure for international ransomware group LockBit, the UK’s National Crime Agency (NCA) revealed on Tuesday, and will repurpose the technology to expose the group’s operations to the world.The joint operation, between the NCA, the FBI, Europol and a coalition of international police agencies, was first revealed with a post on LockBit’s own website, which read: “This site is now under the control of the National Crime Agency of the UK, working in close cooperation with the FBI and the international law enforcement taskforce Operation Cronos.” Continue reading...
US adversaries employ generative AI in attempted cyberattack
20 February 2024
A recent report reveals how cyberattacks utilizing AI technology were carried out by state adversaries, highlighting the global threat landscape and importance of cybersecurity vigilance.
LockBit Ransomware Operation Shut Down; Criminals Arrested; Decryption Keys Released
20 February 2024
The U.K. National Crime Agency (NCA) on Tuesday confirmed that it obtained LockBit's source code as well as intelligence pertaining to its activities and their affiliates as part of a dedicated task force called Operation Cronos.
"Some of the data on LockBit's systems belonged to victims who had paid a ransom to the threat actors, evidencing that even when a ransom is paid, it does not
NCSC statement on law enforcement's disruption of lockbit ransomware operation
20 February 2024
The National Crime Agency (NCA) has announced that it is conducting a months-long campaign with international partners to disrupt the threat posed by the Lockbit ransomware operation.
New Malicious PyPI Packages Caught Using Covert Side-Loading Tactics
20 February 2024
Cybersecurity researchers have discovered two malicious packages on the Python Package Index (PyPI) repository that were found leveraging a technique called DLL side-loading to circumvent detection by security software and run malicious code.
The packages, named NP6HelperHttptest and NP6HelperHttper, were each downloaded 537 and 166 times, respectively,
NCSC statement on law enforcement's distribution of lockbit ransomware operation
20 February 2024
The National Crime Agency (NCA) has announced that it is conducting a months-long campaign with international partners to disrupt the threat posed by the Lockbit ransomware operation.
Hackers Exploit Critical RCE Flaw in Bricks WordPress Site Builder
20 February 2024
The vulnerability, tracked as CVE-2024-25600, was discovered by a researcher named 'snicco' and a fix became available on February 13 with the release of version 1.9.6.1.
Cactus Ransomware Gang Claims the Theft of 1.5TB of Data From Schneider Electric
20 February 2024
The attack, which hit the Sustainability Business division on January 17th, caused outages in Schneider Electric’s Resource Advisor cloud platform. The gang published 25MB of stolen data as proof of the hack.
New Report Reveals North Korean Hackers Targeting Defense Firms Worldwide
20 February 2024
The North Korean state-sponsored threat actors have been attributed to a cyber espionage campaign targeting the defense sector across the world.
In a joint advisory published by Germany's Federal Office for the Protection of the Constitution (BfV) and South Korea's National Intelligence Service (NIS), the agencies said the goal of the attacks is to plunder advanced defense technologies in a "
Learn How to Build an Incident Response Playbook Against Scattered Spider in Real-Time
20 February 2024
In the tumultuous landscape of cybersecurity, the year 2023 left an indelible mark with the brazen exploits of the Scattered Spider threat group. Their attacks targeted the nerve centers of major financial and insurance institutions, culminating in what stands as one of the most impactful ransomware assaults in recent memory.
When organizations have no response plan in place for such an
SaaS Compliance through the NIST Cybersecurity Framework
20 February 2024
The US National Institute of Standards and Technology (NIST) cybersecurity framework is one of the world's most important guidelines for securing networks. It can be applied to any number of applications, including SaaS.
One of the challenges facing those tasked with securing SaaS applications is the different settings found in each application. It makes it difficult to develop a
Critical Flaws Found in ConnectWise ScreenConnect Software - Patch Now
20 February 2024
ConnectWise has released software updates to address two security flaws in its ScreenConnect remote desktop and access software, including a critical bug that could enable remote code execution on affected systems.
The vulnerabilities, which currently lack CVE identifiers, are listed below -
Authentication bypass using an alternate path or channel (CVSS score: 10.0)
Improper limitation of
Google Open Sources Magika: AI-Powered File Identification Tool
20 February 2024
Magika outperforms conventional methods and is used to enhance user safety in Gmail, Drive, and Safe Browsing. Google emphasizes the use of AI to strengthen digital security and shift the balance in favor of defenders in cybersecurity.
Meta Warns of 8 Spyware Firms Targeting iOS, Android, and Windows Devices
20 February 2024
The surveillance industry continues to evolve, with recent discoveries of new surveillance tools like Patternz and a previously unknown mobile network attack called MMS Fingerprint, raising concerns about privacy and security.
Newly Discovered RustDoor Malware Impersonates Visual Studio Update
20 February 2024
A new macOS malware dubbed RustDoor, written in Rust, is being distributed disguised as a Visual Studio update. The malware provides backdoor access to compromised systems and is linked to infrastructure associated with the BlackCat ransomware gang. Researchers have shared a list of known IOCs associated with RustDoor, which includes binaries, download domains, and URLs.
WordPress Bricks Theme Under Active Attack: Critical Flaw Impacts 25,000+ Sites
20 February 2024
A critical security flaw in the Bricks theme for WordPress is being actively exploited by threat actors to run arbitrary PHP code on susceptible installations.
The flaw, tracked as CVE-2024-25600 (CVSS score: 9.8), enables unauthenticated attackers to achieve remote code execution. It impacts all versions of the Bricks up to and including 1.9.6.
It has been addressed by the theme developers in&
New 'MMS Fingerprinting' Zero-Click Attack Used to Deploy Spyware
20 February 2024
The "MMS Fingerprint" technique leverages the MMS flow to retrieve user device information, which could be used to tailor malicious payloads like Pegasus spyware or craft more effective phishing campaigns.
‘M.O.R.E’ Ransomware Emerges on the Dark Web; Threatens Windows, Mac, Linux Users
20 February 2024
Multi-OS Ransomware Executable (M.O.R.E) represents a new breed of ransomware that can target multiple operating systems simultaneously, posing a significant threat to cybersecurity.
Iran and Hezbollah Hackers Launch Attacks to Influence Israel-Hamas Narrative
20 February 2024
Hackers backed by Iran and Hezbollah staged cyber attacks designed to undercut public support for the Israel-Hamas war after October 2023.
This includes destructive attacks against key Israeli organizations, hack-and-leak operations targeting entities in Israel and the U.S., phishing campaigns designed to steal intelligence, and information operations to turn public opinion against Israel.
Iran
LockBit Ransomware's Darknet Domains Seized in Global Law Enforcement Raid
20 February 2024
An international law enforcement operation has led to the seizure of multiple darknet domains operated by LockBit, one of the most prolific ransomware groups, marking the latest in a long list of digital takedowns.
While the full extent of the effort, codenamed Operation Cronos, is presently unknown, visiting the group's .onion website displays a seizure banner containing the message "