Latest Cybersecurity News and Articles
Asset Management Firm Armis Acquires Honeypot Maker CTCI
15 February 2024
Armis acquired CTCI, a cybersecurity startup, in a deal worth nearly $20 million. The acquisition aims to integrate CTCI's technology into Armis' Centrix platform to enhance early warning cyber intelligence capabilities.
Cybercriminals found innovative ways to infect endpoints in 2023
15 February 2024
Attack methods used by cybercriminals in Q4 of 2023 reveal evolving trends.
ALPHV Ransomware Claims Hit on Canada’s Trans-Northern Pipelines
15 February 2024
TNPI's internal network was breached by the ALPHV/BlackCat ransomware gang, leading to the potential theft of 183GB of company documents and contact information for TNPI employees.
Two Queens Men Sentenced for Hacking Into JFK Airport Taxi Dispatch System
15 February 2024
Two men, Daniel Abayev and Peter Leyman, were sentenced to prison for hacking into the taxi dispatch system at JFK Airport in New York City. They exploited the system to allow certain drivers to skip ahead in the pickup line in exchange for payment.
How Nation-State Actors Target Your Business: New Research Exposes Major SaaS Vulnerabilities
15 February 2024
With many of the highly publicized 2023 cyber attacks revolving around one or more SaaS applications, SaaS has become a cause for genuine concern in many boardroom discussions. More so than ever, considering that GenAI applications are, in fact, SaaS applications.
Wing Security (Wing), a SaaS security company, conducted an analysis of 493 SaaS-using companies in Q4 of 2023. Their study
Romantic AI Chatbots Fail the Security and Privacy Test
15 February 2024
Most relationship chatbots lack transparency on security management, encryption use, and data privacy, raising concerns about the potential for data misuse and manipulation of users.
Update: LockBit Claims Ransomware Attack on Fulton County, Georgia
15 February 2024
The county's website still shows the initial alert about the system outage, and some services, like property tax and water billing, remain offline. The hackers claim to have stolen sensitive data and threaten to release it if a ransom is not paid.
Cybercriminals Get Productivity Boost With AI
15 February 2024
Cybercriminals are using generative AI tools to create convincing face swaps and exploit loopholes in biometric systems, posing a significant threat to identity verification.
New Critical Microsoft Exchange Bug Exploited as Zero-Day
15 February 2024
Discovered internally and tracked as CVE-2024-21410, this security flaw can let remote unauthenticated threat actors escalate privileges in NTLM relay attacks targeting vulnerable Microsoft Exchange Server versions.
Chinese Hackers Using Deepfakes in Advanced Mobile Banking Malware Attacks
15 February 2024
A Chinese-speaking threat actor codenamed GoldFactory has been attributed to the development of highly sophisticated banking trojans, including a previously undocumented iOS malware called GoldPickaxe that's capable of harvesting identity documents, facial recognition data, and intercepting SMS.
"The GoldPickaxe family is available for both iOS and Android platforms,"
OpenAI Shuts Down Accounts Linked to Five Nation-State Hacking Groups
15 February 2024
State-linked hacking groups from China, Russia, Iran, and North Korea were observed using AI technologies to improve reconnaissance, command techniques, and social engineering efforts, posing a potential cybersecurity threat.
France Uncovers Russian Disinformation Campaign
15 February 2024
The network of disinformation websites, dubbed "Portal Kombat," reproduces content from pro-Russian social media accounts and news agencies, using automation and machine translation to disseminate the content.
Water Hydra’s Zero-Day Attack Chain Targets Financial Traders
15 February 2024
The Water Hydra APT group utilized CVE-2024-21412 to bypass Microsoft Defender SmartScreen and implant victims with the DarkMe malware, targeting financial market traders.
Zoom Patches Critical Privilege Elevation Flaw in Windows Apps
15 February 2024
The Zoom desktop and VDI clients, as well as the Meeting SDK for Windows, are vulnerable to an improper input validation flaw, which could allow an unauthenticated attacker to conduct privilege escalation on the target system over the network.
Critical Exchange Server Flaw (CVE-2024-21410) Under Active Exploitation
15 February 2024
Microsoft on Wednesday acknowledged that a newly disclosed critical security flaw in Exchange Server has been actively exploited in the wild, a day after it released fixes for the vulnerability as part of its Patch Tuesday updates.
Tracked as CVE-2024-21410 (CVSS score: 9.8), the issue has been described as a case of privilege escalation impacting the Exchange Server.
"An attacker
Power grab: the hidden costs of Ireland’s datacentre boom
15 February 2024
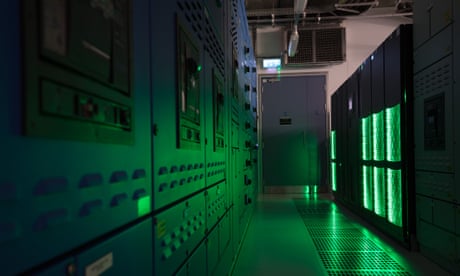 Datacentres are part of Ireland’s vision of itself as a tech hub. There are now more than 80, using vast amounts of electricity. Have we entrusted our memories to a system that might destroy them?In the doldrum days between Christmas and New Year, we take a family trip to see a datacentre. Over the past two decades, datacentres have become a common sight on the outskirts of Dublin and many other Irish cities and towns. Situated in industrial business parks, they are easy to miss. But these buildings are critical to the maintenance of contemporary life: inside their walls stand rows and rows of networked servers; inside the servers, terabytes of data flow.It’s a seven-minute drive from where we live now in Artane, Dublin, to the Clonshaugh datacentre, situated in a business park behind Northside shopping centre. Although we live close by, we haven’t driven this way before, and our route takes us through a number of the local authority estates that my husband lived in as a boy. These estates are set on either side of a long, straight road pocked with chicanes to deter joyriders. Even though the housing development sprawls for miles on either side – with large wind-blasted green spaces in between – the houses huddle, squashed together. It looks as if someone has transplanted a warren of inner-city Victorian terraces to this desolate terrain. Continue reading...
Report reveals the 5 fraud threats to watch out for in 2024
14 February 2024
The report discusses the five fraud threats that are predicted to emerge in 2024.
Phishing attacks increased 106% year over year
14 February 2024
According to a recent threat report, detections of phishing attempts increased by 106% year-over-year, while malware detections were up 40%.
The FBI warns of the prevalence of romance scams this Valentine's Day
14 February 2024
This Valentine's Day, the FBI warns online users about romance scams and the associated losses.
Kent Goodrow appointed Chief Information Security Officer at Systems Engineering
14 February 2024
Kent Goodrow has been appointed Chief Information Security Officer at Systems Engineering. Goodrow is pursuing a Master's in Cybersecurity Management.