Latest Cybersecurity News and Articles
Large-Scale Campaign Delivers Proxy Server App to Make Systems Serve as Residential Exit Nodes
17 August 2023
The proxy application is silently installed by malware on infected systems without user knowledge or interaction, and it goes undetected by anti-virus software as it is signed.
Malvertisers up Their Game Against Researchers
17 August 2023
Threat actors are using advanced cloaking techniques in malvertising campaigns to remain undetected and drop malware, making it more challenging for defenders to identify and report these incidents.
Ongoing Hijacking Campaign Targets LinkedIn Accounts
17 August 2023
Several LinkedIn users have reported difficulties in recovering their hacked or locked-out accounts through LinkedIn support. Some claimed to have faced ransom demands or account deletion threats. In the past few months, according to Google Trends, there’s been a 5000% increase in searches related to LinkedIn account hacks and recovery.
AWS Customers’ Most Common Security Mistake
17 August 2023
Misconfigurations play a central and persistent role in cyber intrusions. According to Google Cloud research released earlier this month, poor identity and access management is directly linked to more than 3 in 5 compromises in the cloud.
Russian Hackers Use Zulip Chat App for Covert C&C in Diplomatic Phishing Attacks
17 August 2023
An ongoing campaign targeting ministries of foreign affairs of NATO-aligned countries points to the involvement of Russian threat actors.
The phishing attacks feature PDF documents with diplomatic lures, some of which are disguised as coming from Germany, to deliver a variant of a malware called Duke, which has been attributed to APT29 (aka BlueBravo, Cloaked Ursa, Cozy Bear, Iron Hemlock,
Raccoon Stealer Returns with New Evasion Capabilities
17 August 2023
After a 6-month hiatus, the developers behind the notorious Raccoon Stealer information-stealing malware have reintroduced version 2.3.0 to cybercriminal forums. Its enhanced features include a quick search tool, anti-suspicion measures against security-assisting bots, IP reporting to deter monitoring, and a log stats panel.
A Third of UK University Students Targeted By Fraud
17 August 2023
One in three students at British universities encountered fraud attempts online last year, according to a new study from NatWest. A third of respondents said they’d encountered a scam over the previous 12 months.
Public Sector Hit in Sudden Surge, Reveals New Report
17 August 2023
A BlackBerry threat intelligence report revealed a 40% rise in cyberattacks against government and public service entities versus the previous quarter. This includes public transit, utilities, schools, and other government services we rely on daily.
How Disjoined Threat Intelligence Limits Companies — And What to do About it
17 August 2023
Threat intelligence is more abundant than ever. The information defenders can use to hunt, prepare for and counter potential threats isn’t hard to find, but it is fragmented.
Ransomware: To Pay or Not to Pay
17 August 2023
The best strategy against ransomware attacks is a combination of robust defenses to protect assets and a focus on resilience and flexibility to minimize disruptions and respond effectively to incidents.
PDF Lures Aimed at NATO Countries Contain a Russian Clue
17 August 2023
One of the PDFs delivered a variant of Duke, malware that has been linked to Russian state-sponsored cyber-espionage activities of APT29, also known as Nobelium, Cozy Bear, and The Dukes.
Global IoT Trust Survey Reveals Security Concerns
17 August 2023
A report, Circles of Trust 2023: Exploring Consumer Trust in the Digital Society, published by Utimaco, suggests only 14% of consumers view smart devices as secure, despite 38% using them.
CISA Warns of Critical Citrix ShareFile Flaw Exploited in the Wild
17 August 2023
CISA is warning that a critical Citrix ShareFile secure file transfer vulnerability tracked as CVE-2023-24489 is being targeted by unknown actors and has added the flaw to its catalog of known security flaws exploited in the wild.
Google Introduces First Quantum Resilient FIDO2 Security Key Implementation
17 August 2023
The development comes less than a week after the tech giant said it plans to add support for quantum-resistant encryption algorithms in Chrome 116 to set up symmetric keys in TLS connections.
If there is a lesson from the NI police data breach it is not to forget the cruelty of the Troubles | Martin Kettle
17 August 2023
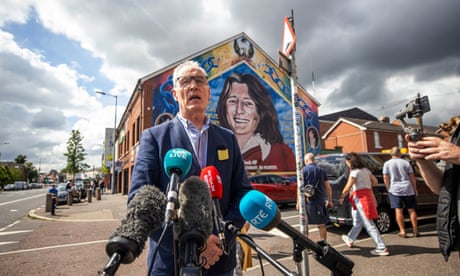 The leak could undermine security in Northern Ireland – restoring power sharing is a political necessity at this momentHalf of the people who live in these islands have no adult memory at all of the Northern Ireland troubles. Too many of those who can remember them have allowed the bombings, shootings, riots and violence to slip from their minds in the 25 years that have passed since a peace treaty was signed in 1998. But last week’s data leak by the Police Service of Northern Ireland (PSNI) ought to be a wake-up call for the forgetful, and a lightbulb moment for the unaware.Nine days ago, in response to a freedom of information request whose provenance remains unclear, someone in the PSNI mistakenly put the names, initials, ranks, place of work and departments of all of its 10,000 officers and staff online for about three hours before they were removed. Especially in a profession where police and their families were, and sometimes still are, regular targets, it was a spectacular security breach, even in these more peaceful times.Martin Kettle is a Guardian columnist Continue reading...
Unveiling the Sophisticated Statc Stealer
17 August 2023
Zscaler ThreatLabz detected and dissected Statc Stealer, a potent information-stealing malware targeting Windows systems. This C++-based malware effectively extracts sensitive data from popular web browsers, cryptocurrency wallets, and messaging apps like Telegram. To counteract the risks, the implementation of several proactive strategies such as education and awareness, robust antivirus solutions, and network monitoring, among others, is essential.
CISA Adds Citrix ShareFile Flaw to KEV Catalog Due to In-the-Wild Attacks
17 August 2023
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical security flaw in Citrix ShareFile storage zones controller to its Known Exploited Vulnerabilities (KEV) catalog, based on evidence of active in-the-wild exploitation.
Tracked as CVE-2023-24489 (CVSS score: 9.8), the shortcoming has been described as an improper access control bug that, if successfully exploited
70% of web applications have severe security gaps
16 August 2023
According to a CyCognito report, 74% of assets with personally identifiable information (PII) are vulnerable to at least one known major exploit.
Major U.S. Energy Organization Targeted in QR Code Phishing Attack
16 August 2023
According to Cofense, who spotted this campaign, this is the first time that QR codes have been used at this scale, indicating that more phishing actors may be testing their effectiveness as an attack vector.
Chrome 116 Patches 26 Vulnerabilities
16 August 2023
Google on Tuesday announced the release of Chrome 116 to the stable channel with patches for 26 vulnerabilities, including 21 reported by external researchers. Of the externally reported bugs, eight have a severity rating of ‘high.’